Step 4: Prove
What should an AI audit trail record?
For every AI action: which agent acted, what it did, who approved it, when, and what it cost. Entries cannot be edited.
- Append-only
- Who approved
- What it cost
Interactive example
Open an entry
Select a row to see its details.
- Agent
- Follow-up drafter
- Action
- Send follow-up email
- Approved by
- Named approver
- When
- Date and time of the decision
- Cost
- Work Units for this action
- Agent
- Weekly summary
- Action
- Build summary
- Approved by
- Not needed, stays inside MFDIO
- When
- Date and time it ran
- Cost
- Work Units for this action
- Agent
- Unknown agent
- Action
- Blocked
- Approved by
- Not applicable
- When
- Date and time it was blocked
- Cost
- No action taken
Example entries. Illustrative, not real data. Click a row.
Every entry
Five fields, always
Agent
Action
Approver
Time
Cost
In the product
The record
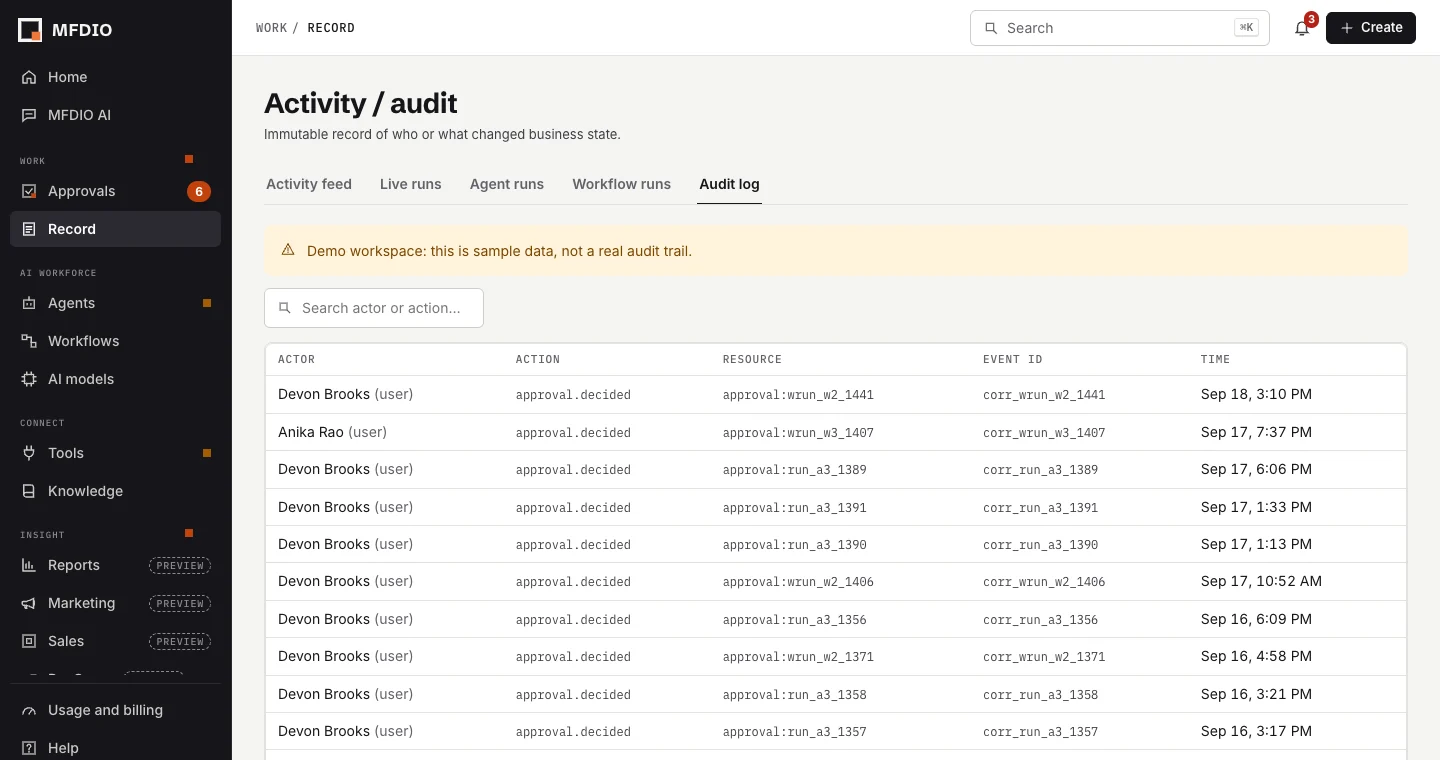
- One list of who did what
- Entries cannot be edited
- Sample data is labeled
Status
Today Works now
- Append-only record of runs, changes and approvals
- Who and when on every entry
- Cost per action in Work Units
Roadmap Planned
- Reports on live data from connected systems
Quick answers
Does an audit trail make us compliant?
No. It is evidence, not a certification. MFDIO makes no compliance guarantee and does not hold SOC 2 or ISO 27001 today.
Can entries be changed?
No. The audit table is append-only, enforced in the database.